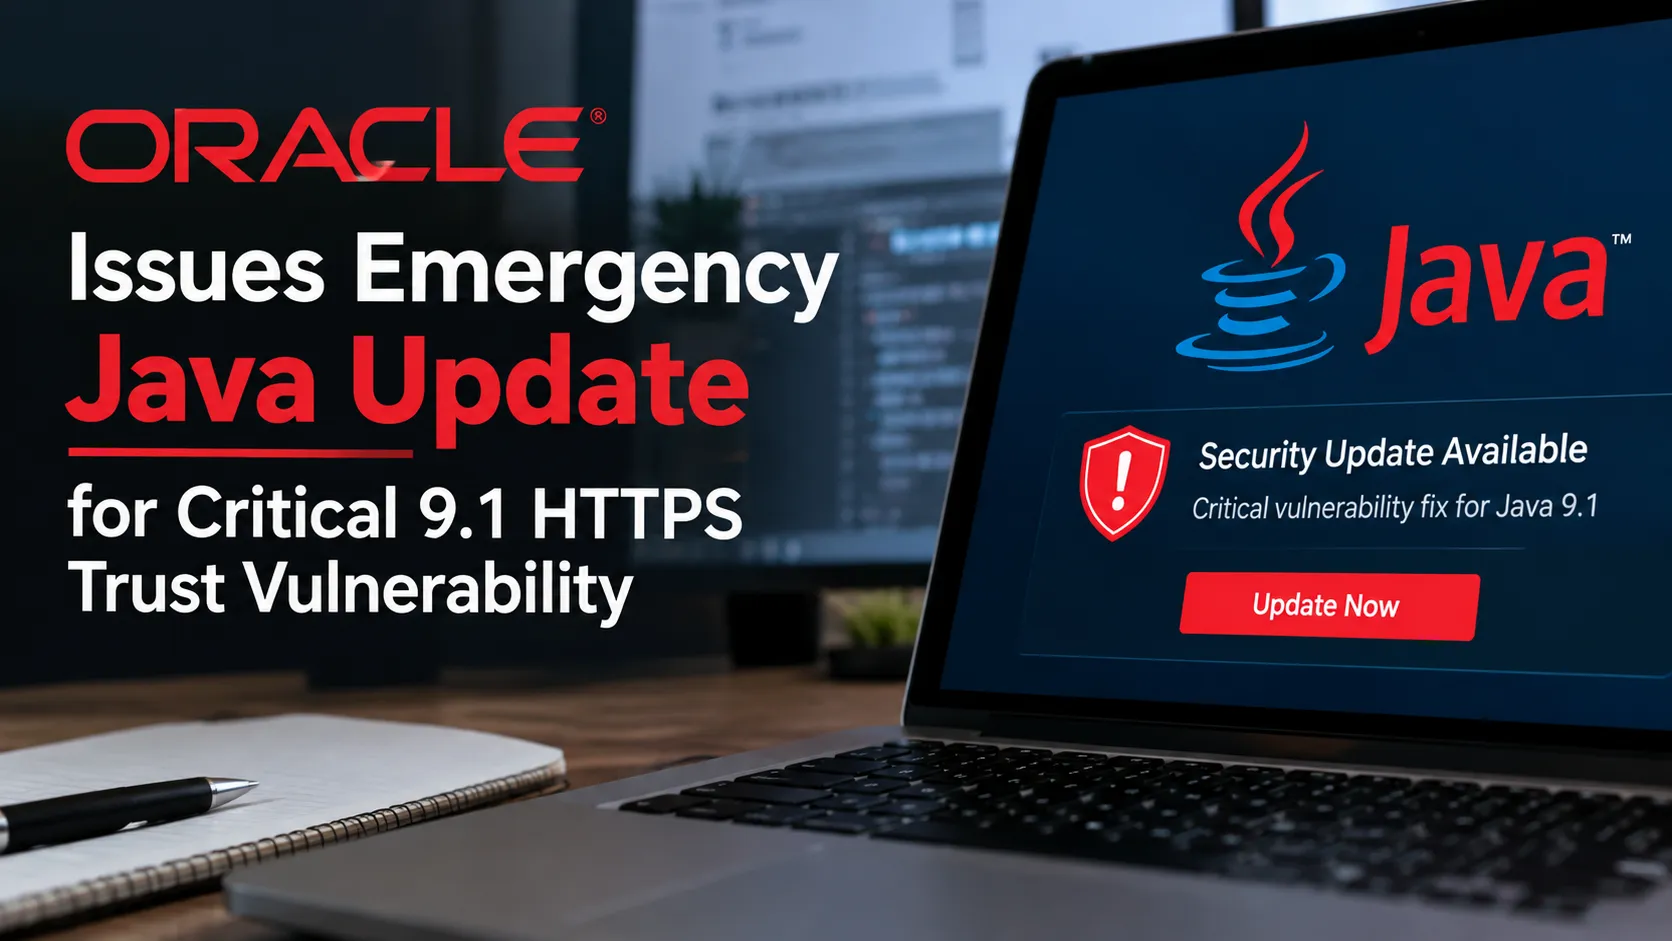
Tech giant Oracle has released an urgent emergency security update to fix a critical vulnerability affecting Java applications. Tracked as CVE 2026 91403 this security flaw has been given a very high severity score of 9.1 out of 10. The dangerous bug impacts the Java Secure Socket Extension (JSSE) component which handles how Java programs trust digital certificates and secure web connections.
According to cybersecurity experts hackers can exploit this flaw remotely over the network without needing any password login credentials or user interaction. If exploited attackers could trick software into trusting fake or fraudulent certificates potentially stealing sensitive user data. The issue stems from certain weak intermediate certificates linked to eMudhra. To solve this Oracle emergency patch does not disable HTTPS. Instead it updates the system to automatically distrust those compromised intermediate certificates.
IT teams developers and system administrators worldwide are strongly advised to check their software systems update their Java SE and GraalVM versions immediately or apply the recommended security configurations to keep their networks safe from potential cyberattacks.