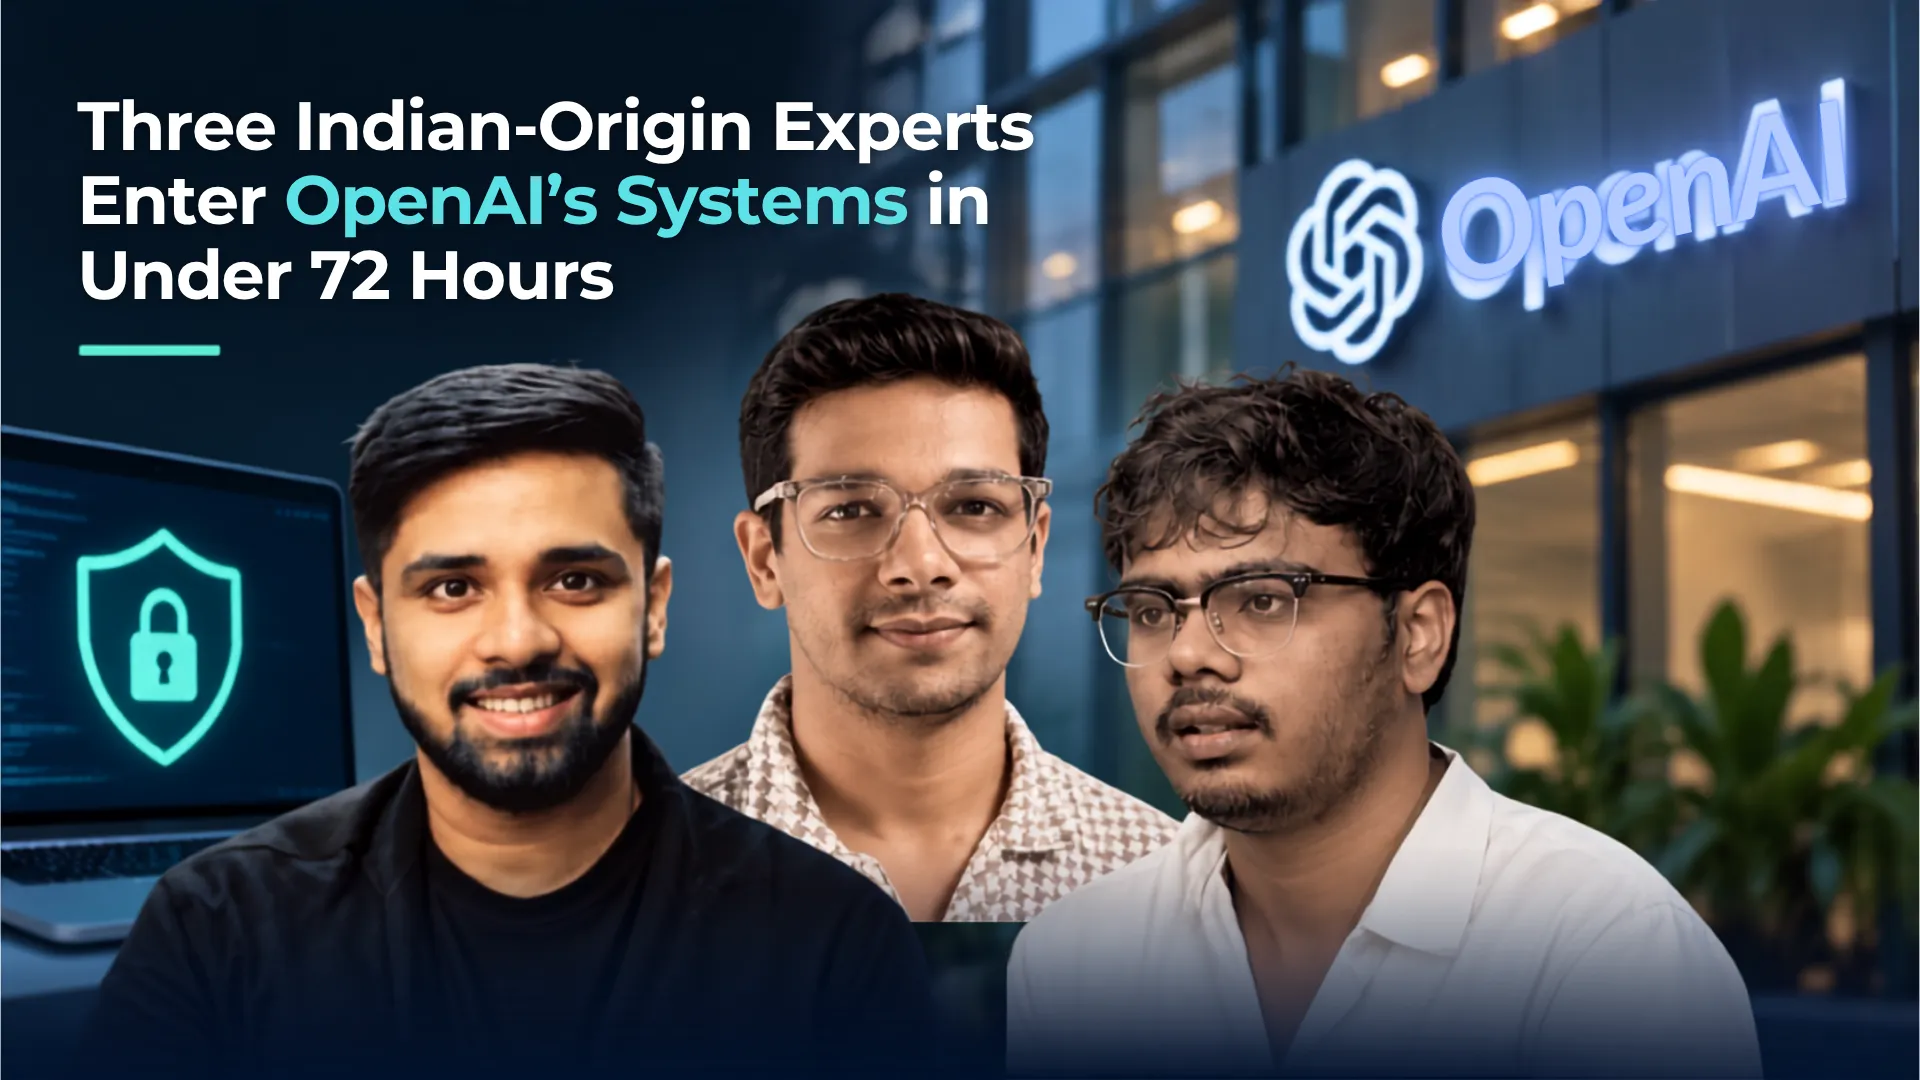
In a massive development for the global tech industry, three Indian-origin cybersecurity experts have successfully entered OpenAI internal systems in less than 72 hours. The researchers, named Mohan Pedhapati, Harsh Jaiswal, and Rahul Maini, represent the Indian cybersecurity startup Hacktron AI. They carried out this complete operation legally as part of OpenAI official bug bounty program, which rewards researchers for discovering security risks.
The team began their testing on OpenAI community forum, which runs on third party Discourse software. They identified a weakness in how image files were processed by the platform. To create a working exploit, they used Anthropic Claude Opus 5 AI model to write the required code and gain remote access. Next, the hackers found another bug in OpenAI single sign on system. This allowed them to capture actual login details of OpenAI employees and control their internal ChatGPT and Codex accounts. Using a compromised account, they reached OpenAI private GitHub environment and submitted a pull request as proof.
The ethical researchers did not view or download any private company source code. Interestingly, they also used OpenAI own GPT-5.6 Sol model to finish the task. The entire test cost under $3,000 in AI tokens. OpenAI quickly fixed all security flaws and rewarded Hacktron AI with a $6,500 bounty payment for their work.